CompassMSP Closes the Loop between IT Operations and Cybersecurity So Findings Become Fixes
The Silicon Review
Most organizations do not lack security findings. They lack the capacity to act on them. A vulnerability gets identified, a patch is required, an access control needs adjustment, and then progress stalls because the team that detected the issue is not the team responsible for the systems involved. Detection vendors report. IT teams operate. When those functions sit in separate silos with separate documentation and separate escalation paths, findings accumulate faster than remediation occurs, and the gap between what an organization knows and what it has actually fixed becomes its real exposure.
CompassMSP was built to eliminate that gap. The company operates as a managed service provider and security partner serving growing, mid-sized, and regulated organizations, with more than 350 technical experts, over 25 U.S. locations, and a 100 percent in-house security operations center providing 24/7 monitoring and response. Its service range spans managed IT, cybersecurity and advisory, compliance and risk management, cloud and infrastructure, unified communications, IT modernization, and secure AI enablement, all delivered through a closed-loop delivery model that connects detection to action rather than treating them as separate functions.
The distinction matters because the market increasingly punishes delay. Verizon's 2026 Data Breach Investigations Report found that 31 percent of analyzed breaches involved a third party, up 60 percent from the prior report, while IBM's 2026 Cost of a Data Breach Report identified $1.33 million in higher average breach costs when identification and containment exceeded 200 days. CompassMSP's operating model addresses precisely that variable: the time between knowing something is wrong and confirming it has been fixed.
Closed-Loop Delivery as an Operating Discipline
CompassMSP's defining capability is its Command Center model, which gives support, security, cloud, communications, and advisory teams shared context about a client's environment, priorities, and risk. When a security finding requires a patch, an access change, or a network update, ownership is defined and escalation is coordinated rather than improvised. The model supports continuous threat exposure management, an ongoing cycle of identifying weaknesses, prioritizing them by business impact, validating potential exposure, and confirming that remediation worked. For clients, the outcome is measurable. Telescope Health reported 80 percent fewer outages following infrastructure improvements and dedicated support from CompassMSP, evidence that coordinated operations produce reliability gains alongside security posture improvements.
Right-Sized Engagement without Service Bloat
CompassMSP allows organizations to start with the services addressing immediate priorities and expand as needs evolve. Fully managed IT provides ongoing operational ownership while co-managed IT adds capacity alongside internal teams. Essentials security is included by default, with additional cybersecurity and advisory capabilities available as requirements grow. That structure avoids the common enterprise pattern where organizations purchase capability they never deploy. For mid-sized businesses with constrained budgets, the ability to sequence investment, starting with IT support or compliance readiness before layering advanced detection, makes security spending defensible rather than aspirational.
Compliance as a Demonstrable Function
CompassMSP supports assessment, remediation planning, and audit preparation across frameworks including CMMC, HIPAA, HITRUST, SOC 2, PCI DSS, and NYDFS 500, with scope tailored to each organization. Compliance work connects regulatory requirements to the systems, controls, and records that substantiate them, which is the difference between claiming compliance and demonstrating it. For organizations in healthcare, financial services, and legal services, sectors where audit failures carry direct financial and legal consequences, that capability reduces exposure that insurance cannot cover.
Strategic Guidance Embedded in the Engagement
Every CompassMSP engagement includes virtual CIO and virtual CISO advisory. The vCIO connects technology gaps, lifecycle requirements, business priorities, and budget planning into a living 12-to-24-month roadmap. The vCISO prioritizes security risk, plans investment, strengthens governance, and translates progress for executives and boards. That combination addresses a persistent gap in mid-market organizations, which require strategic technology leadership but cannot justify full-time executive hires. Embedding that guidance into the service relationship makes strategy continuous rather than episodic.
Security-First Architecture as Standard Practice
CompassMSP architects solutions using CIS and NIST frameworks, implements zero-trust access controls with continuous verification, and maintains proactive vulnerability hunting as standard practice rather than a premium add-on. The company's 100 percent in-house security operations center provides 24/7 managed detection and response across endpoints, identities, networks, and cloud environments, with AI-assisted triage validated by human analysts. For clients, that structure means security is present in the architecture from day one rather than retrofitted after an incident.
Leadership Rooted in Operational Experience
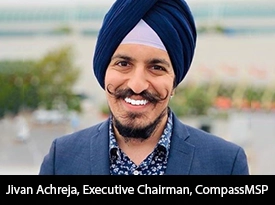
Jivan Achreja serves as Executive Chairman of CompassMSP, guiding a leadership team that brings decades of experience across managed IT, cybersecurity, cloud infrastructure, and compliance. The company's leadership philosophy centers on knowing the way, going the way, and showing the way, with executives expected to own results, remain present, and guide teams through change with clarity and confidence. That orientation has shaped CompassMSP's approach to acquisitions and integration as well. The firm brings the perspective of an operator, acquirer, and long-term technology partner, having worked through diligence windows, Day 1 deadlines, and post-close execution across its own expanding organization. For clients, that experience translates into guidance grounded in practical operational reality rather than theoretical frameworks.
Jivan Achreja, Executive Chairman