Digital Velocity: Leading the Next Evolution of Cybersecurity and AI Governance
The Silicon Review
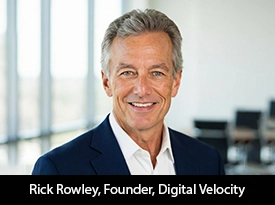
Digital Velocity is a forward-thinking virtual CISO, cybersecurity, and AI governance advisory firm founded by Rick Rowley to help organizations navigate an increasingly complex digital and risk landscape. Rowley’s decision to build the company was shaped by his own experience working within a large systems integrator, where he became increasingly frustrated with a weak strategic compass and the limitations of the traditional consulting model. After leaving in 2023, he founded Digital Velocity as a virtual CISO organization, initially focused on giving businesses access to experienced security leadership without the cost and commitment of a full-time executive hire. Over time, the firm evolved into a full-service consultancy spanning CISO advisory, cybersecurity, AI governance, and risk management. For Rowley, however, the journey has been about more than building a company. He describes the most rewarding aspect as the personal growth that has come through the experience, particularly the daily encounters, challenges, and relationships that continually push him to learn, adapt, and evolve.
Today, Digital Velocity works with organizations seeking practical, senior-level guidance to strengthen security programs while embracing emerging technologies with confidence. Its services include fractional CISO advisory, AI governance and risk management, third-party risk programs, and security program management, supported by recognized industry frameworks and standards such as the NIST AI Risk Management Framework, ISO/IEC 42001, OWASP GenAI Top 10, MITRE ATLAS, and the EU AI Act. As organizations rapidly integrate artificial intelligence into their operations, Digital Velocity helps them establish the governance, controls, and infrastructure needed to innovate responsibly. Rather than treating cybersecurity and AI governance as obstacles or compliance exercises, the firm positions digital trust and security as strategic business advantages. By combining experienced security leadership with a practical understanding of AI risk, Digital Velocity enables organizations to move faster while maintaining the controls, accountability, and resilience needed to grow securely.
In conversation with Rick Rowley, Founder of Digital Velocity
You are pioneering the evolution of the CISO role to the Chief Information Security & Digital Trust Officer (CISDTO). How does this innovative expansion of the security mandate create a competitive advantage for your clients in 2026?
The market’s already moving here, which works in my favor; I’m naming a trend rather than inventing one from scratch. CISOs are already stretched thin and organizations need a senior leader who can unify data privacy and security, artificial intelligence and regulatory compliance into one holistic trust strategy. My vision is to build a future where digital trust and innovation scale together.
The risk with any of these industry rebrands we see now is sounding like a title change without operational teeth. CISDTO sits in a smart spot relative to the competing labels; it doesn’t abandon “security” while explicitly absorbing “digital trust” as a business-facing mandate.
The integration of cybersecurity, privacy, and AI governance is a significant challenge for many organizations. How does Digital Velocity’s integrated service model represent a new and innovative approach compared to traditional, siloed consultancies?
An important trend in 2027 will be integration: privacy, security, and AI are no longer assessed independently by regulators. The convergence of cyber risk, operational resilience, and AI governance is pushing organizations away from fragmented, checklist-driven compliance toward a deliberately layered operating model.
Traditional technology advisory firms sell by practice area - a privacy team, a security team, an AI/ML risk team, often with separate partners, separate deliverables, and separate client relationships; their P&L is built around keeping the silos separate. The client ends up overpaying multiple consultancy teams to each partially solve one connected problem, then has to do the integration work themselves.
For client leadership, we provide a single accountable CISDTO-style advisor who can speak fluently across all three domains. Digital Velocity’s structure was designed for convergence from the start, rather than bolting AI governance onto a legacy security practice after the fact, which is what most of our competitors are visibly doing right now.
Your services extend into AI governance and risk management, addressing complex frameworks like the EU AI Act and NIST AI RMF. How is this proactive, consultative innovation helping your clients turn AI compliance into a strategic advantage?
We use NIST AI RMF as the operational engine, and EU AI Act as the legal target. The Act tells a client what they’re liable for; NIST AI RMF gives them the how: the governance, mapping, and measurement functions that produce the technical documentation and risk records the Act actually demands. Clients who only chase the legal checklist end up with paperwork; clients who build the RMF functions get paperwork and a functioning AI risk management capability.
We try to build for a “moderate priority” reality, not just the current deadlines. A path we recommend is a phased-and-sequenced program approach: complete compliance for the highest-risk systems now, develop implementation roadmaps for the rest, and plan around a backstop deadline rather than treating everything as equally urgent. Compliance work done without this sequencing turns into either wasted effort (over-engineering things that received a longer runway) or dangerous gaps (ignoring things that didn’t).
In the fast-moving world of cybersecurity and AI, how do you foster a culture of continuous innovation within your own team to ensure your clients are always ahead of the curve?
We make “test it before you deliver it” a standing practice, not a one-off. Before any new AI or cybersecurity framework or control becomes client-facing, someone on our team has actually built or broken something with it internally.
We build our own standing intelligence loop. We use a lightweight 30-minute biweekly team ritual: scanning what has changed in AI governance, new attack techniques, regulatory movement (e.g., EU AI Act enforcement, state AI laws), and one thing worth updating in our frameworks or deliverables.
We treat every engagement as a source of IP, not just billable hours. After every client engagement, we ask, “What did we build here that should become a template, a one-pager, or a blog post?” That’s literally how our branded deliverables library was built; we make that reflex explicit and repeatable rather than something that happens when we personally have bandwidth.
You emphasize the importance of program management in executing complex AI, cloud, and cybersecurity initiatives. How does your structured, innovation-driven program management methodology de-risk these projects and ensure they deliver transformational value?
Most of our competitors sell either the technical expertise (security architecture, AI controls) or the project management (timelines, status reports); both are rarely integrated. Digital Velocity’s edge is that program management is the risk control: it’s the mechanism that keeps a fast-moving AI or cloud initiative from outrunning its own governance, which is the single most common way these projects go south.
The strongest security, cloud, and AI programs stop defending budget with technical jargon and explain business resilience in terms of financial risk and operational efficiency. A well-run program plan with clear milestones and risk-adjusted timelines is what lets us brief our executive sponsor in terms they can act on and present to business leadership; this is a core piece of the CISDTO positioning we’ve been building.
With the rapid adoption of AI and the increasing complexity of the threat landscape, what is the next frontier of innovation in cybersecurity consulting that Digital Velocity is preparing for?
The frontier has a name, and it arrived faster than expected: Agentic AI security. I’d say our practice is already positioned, and we know where we need to build next:
Trust architecture for shared data models. “What changes when you add trust controls to a shared data model architecture?” is an unsolved problem across the industry right now. The organizations that win will be the ones that capture agentic efficiency while closing the exposure.
Blast-radius containment as a design principle. Isolating agent execution in a sandbox is emerging as a primary technical control for limiting damage when an agent is compromised or misbehaves. For clients, that’s an architecture review question we are well positioned to ask before deployment.
Governance moving inside the product, not just around it. Our new focus is governance embedding directly into agentic products rather than remaining an external compliance layer. That’s how we frame AI governance engagements going forward: less “policy document,” more “controls built into the agent’s operating boundaries.”
What does the future hold for Digital Velocity and its customers? Are exciting things on the way?
I feel the positioning work I’ve been doing is well-timed: our CISDTO framing and the integrated-vs-siloed model across Virtual CISO, AI Governance, and Security Program Management line up with where much of the market is actually moving. AI governance in particular is going from “nice to have” to something InfoSec Teams, boards and regulators are asking about directly, and the EU AI Act briefing I positioned as a next step could be a timely piece if we move on it soon.
Meet the leader behind the success of Digital Velocity
Rick Rowley, Founder
Rick’s information security journey started in a corporate boardroom for a $38 billion multinational financial services company. His team was designing the architecture for a financial transfer application and needed a security framework. When the CIO asked for someone to take the lead, Rick raised his hand knowing he was stepping into new territory. That instinct to lean into the unknown with a relentless technical curiosity has defined his career since.
Nearly two decades later, Rick has moved from hands-on security research and architecture, to securing large-scale enterprise environments, and to multi-year CISO engagements at the board and executive team level. Rick operates at the intersection of business outcomes, cybersecurity, data science, and scalable technology. His current focus is where the CISO role is headed, not just where it’s been. He’s actively defining what he calls the CISDTO (Chief Information Security and Digital Trust Officer), a mandate that folds AI governance, third-party AI risk, and digital trust into the traditional CISO role.
Rick is based in South Florida, with offices in Tampa, Miami, and expanding to Chicago in 2027. He works with organizations navigating the collision of AI adoption and governance, risk management, and the expanding expectations placed on the modern security executive.