Vali Cyber Defends the Layer Attackers Target When They Want to Cripple Everything at Once
The Silicon Review
Security programs typically protect what sits inside the virtual machine. Endpoint agents monitor workloads. Identity controls govern access. Network tools inspect traffic between systems. The hypervisor, the layer underneath all of it, receives comparatively little attention, despite the fact that compromising it grants an attacker control over every workload running above. That asymmetry explains why hypervisor attacks have increased in frequency and why the blast radius of a successful compromise extends far beyond a single system.
Vali Cyber was founded in 2020 to address that specific exposure. The company built ZeroLock, a runtime security platform designed for Linux and its derivatives, with an initial concentration on hypervisors. Its approach differs from conventional security tooling in several respects: it requires no kernel modification, deploys through a single terminal command or a signed VIB via vCenter, and consumes roughly 50MB of RAM. The platform combines prevention controls including command-line multifactor authentication, application filtering, and lockdown rules with AI-driven detection and automated file rollback.
The market context reinforces the urgency. MITRE, an organization with substantial technical resources, suffered a hypervisor attack. Ransomware operators have increasingly targeted ESXi environments because encryption at that layer affects every hosted workload simultaneously. For organizations running virtualized infrastructure, the hypervisor represents a concentration of risk that traditional endpoint and network defenses do not address. Vali Cyber's founding mission, to secure Linux everywhere starting with hypervisors, reflects recognition that the most consequential layer often receives the least protection.
Prevention Controls That Restrict Attacker Movement
ZeroLock's prevention layer extends beyond standard mandatory access controls. The platform provides command-line multifactor authentication, application filtering, process behavior controls, network access controls, file access controls, canary files, and tamper protection. These controls are configurable and can apply universally across a hypervisor environment. Virtual patching addresses existing CVEs in real time, which matters in environments where applying vendor patches requires maintenance windows that operations teams resist. For organizations managing critical uptime requirements, the ability to mitigate known vulnerabilities without immediate patching reduces exposure during the interval between disclosure and remediation.
Detection and Automated Remediation
ZeroLock's AI detection identifies malware in real time, with the company citing greater than 98 percent efficacy against both traditional and fileless ransomware. Detection alone would be insufficient at the hypervisor layer, where manual response cannot keep pace with encryption speed. The platform therefore pairs detection with automated remediation, including file rollback, removal of attacker persistence, and automated process tree termination, without requiring user intervention. That capability addresses the core operational concern for virtualization teams: downtime. An automated response measured in seconds produces a materially different outcome than a manual incident response process measured in hours.
Deployment Flexibility across Hypervisor Platforms
The platform supports VMware ESXi, Nutanix AHV, XenServer, Citrix Hypervisor, Proxmox, Red Hat Enterprise Virtualization, HPE Morpheus, Dell VxRail, and KVM, with ARM-64 support in development. Its API-first architecture enables integration with SIEM and SOAR platforms including Splunk, Sumo Logic, Elastic, and Swimlane, alongside an incident API connection to Veeam. The signed VIB for ESXi allows deployment directly through vCenter, which reduces operational friction for VMware environments and shortens the path from procurement to protection. The absence of kernel modules eliminates a common source of compatibility issues and stability risk.
Recognition and Market Position
Vali Cyber's inclusion in Gartner's Emerging Tech research on security software startups reflects external assessment of the company's approach to a category that larger vendors have addressed inconsistently. The company also maintains a CISO Advisory Board composed of practicing security executives, which provides ongoing feedback on how the platform performs against threats that security leaders actually encounter. For a vendor selling into security organizations, that structure supports both product relevance and credibility with the buyers who evaluate it.
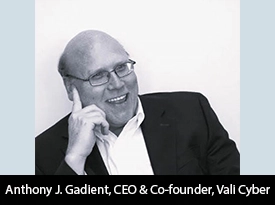
Anthony J. Gadient, CEO and Co-founder
Anthony J. Gadient leads Vali Cyber as CEO and Co-founder. His background includes founding three startups, including Voci Technologies, Renovis Surgical, and Neolinear, with approximately $250 million in successful exits across those ventures. He holds a PhD from Carnegie Mellon University, an MBA from Washington State University, and a BSEE from the University of Virginia. That combination of technical depth and repeated company-building experience shapes Vali Cyber's approach to product development and market positioning as it scales within the hypervisor security category.
The Economics of Hypervisor Security
Vali Cyber's growth reflects escalating demand for protection at a layer that enterprise security programs have historically underweighted. With a platform that prevents attacks through configurable controls, detects threats with AI, remediates automatically, and deploys without kernel modification, the company has established itself among the innovative cybersecurity providers worth watching in 2026. The commercial logic is direct: hypervisor compromise carries disproportionate consequences, traditional defenses do not address that layer, and automation is the only viable response speed against ransomware operating at machine pace. As virtualization remains the foundation of enterprise infrastructure, the case for securing it strengthens.
Anthony J. Gadient, CEO and Co-founder